home › Forums › Device, App & Web Security › Other Web, App Security › Star Media Group Data Breach Exposes NRIC and Passwords
- This topic has 0 replies, 1 voice, and was last updated 3 days, 7 hours ago by
 scamboy.
- Posts
- Star Media Group Berhad, the publisher of Malaysia’s The Star newspaper, has confirmed a data breach involving the theft of personal information, including NRIC numbers, contact details and encrypted account passwords.
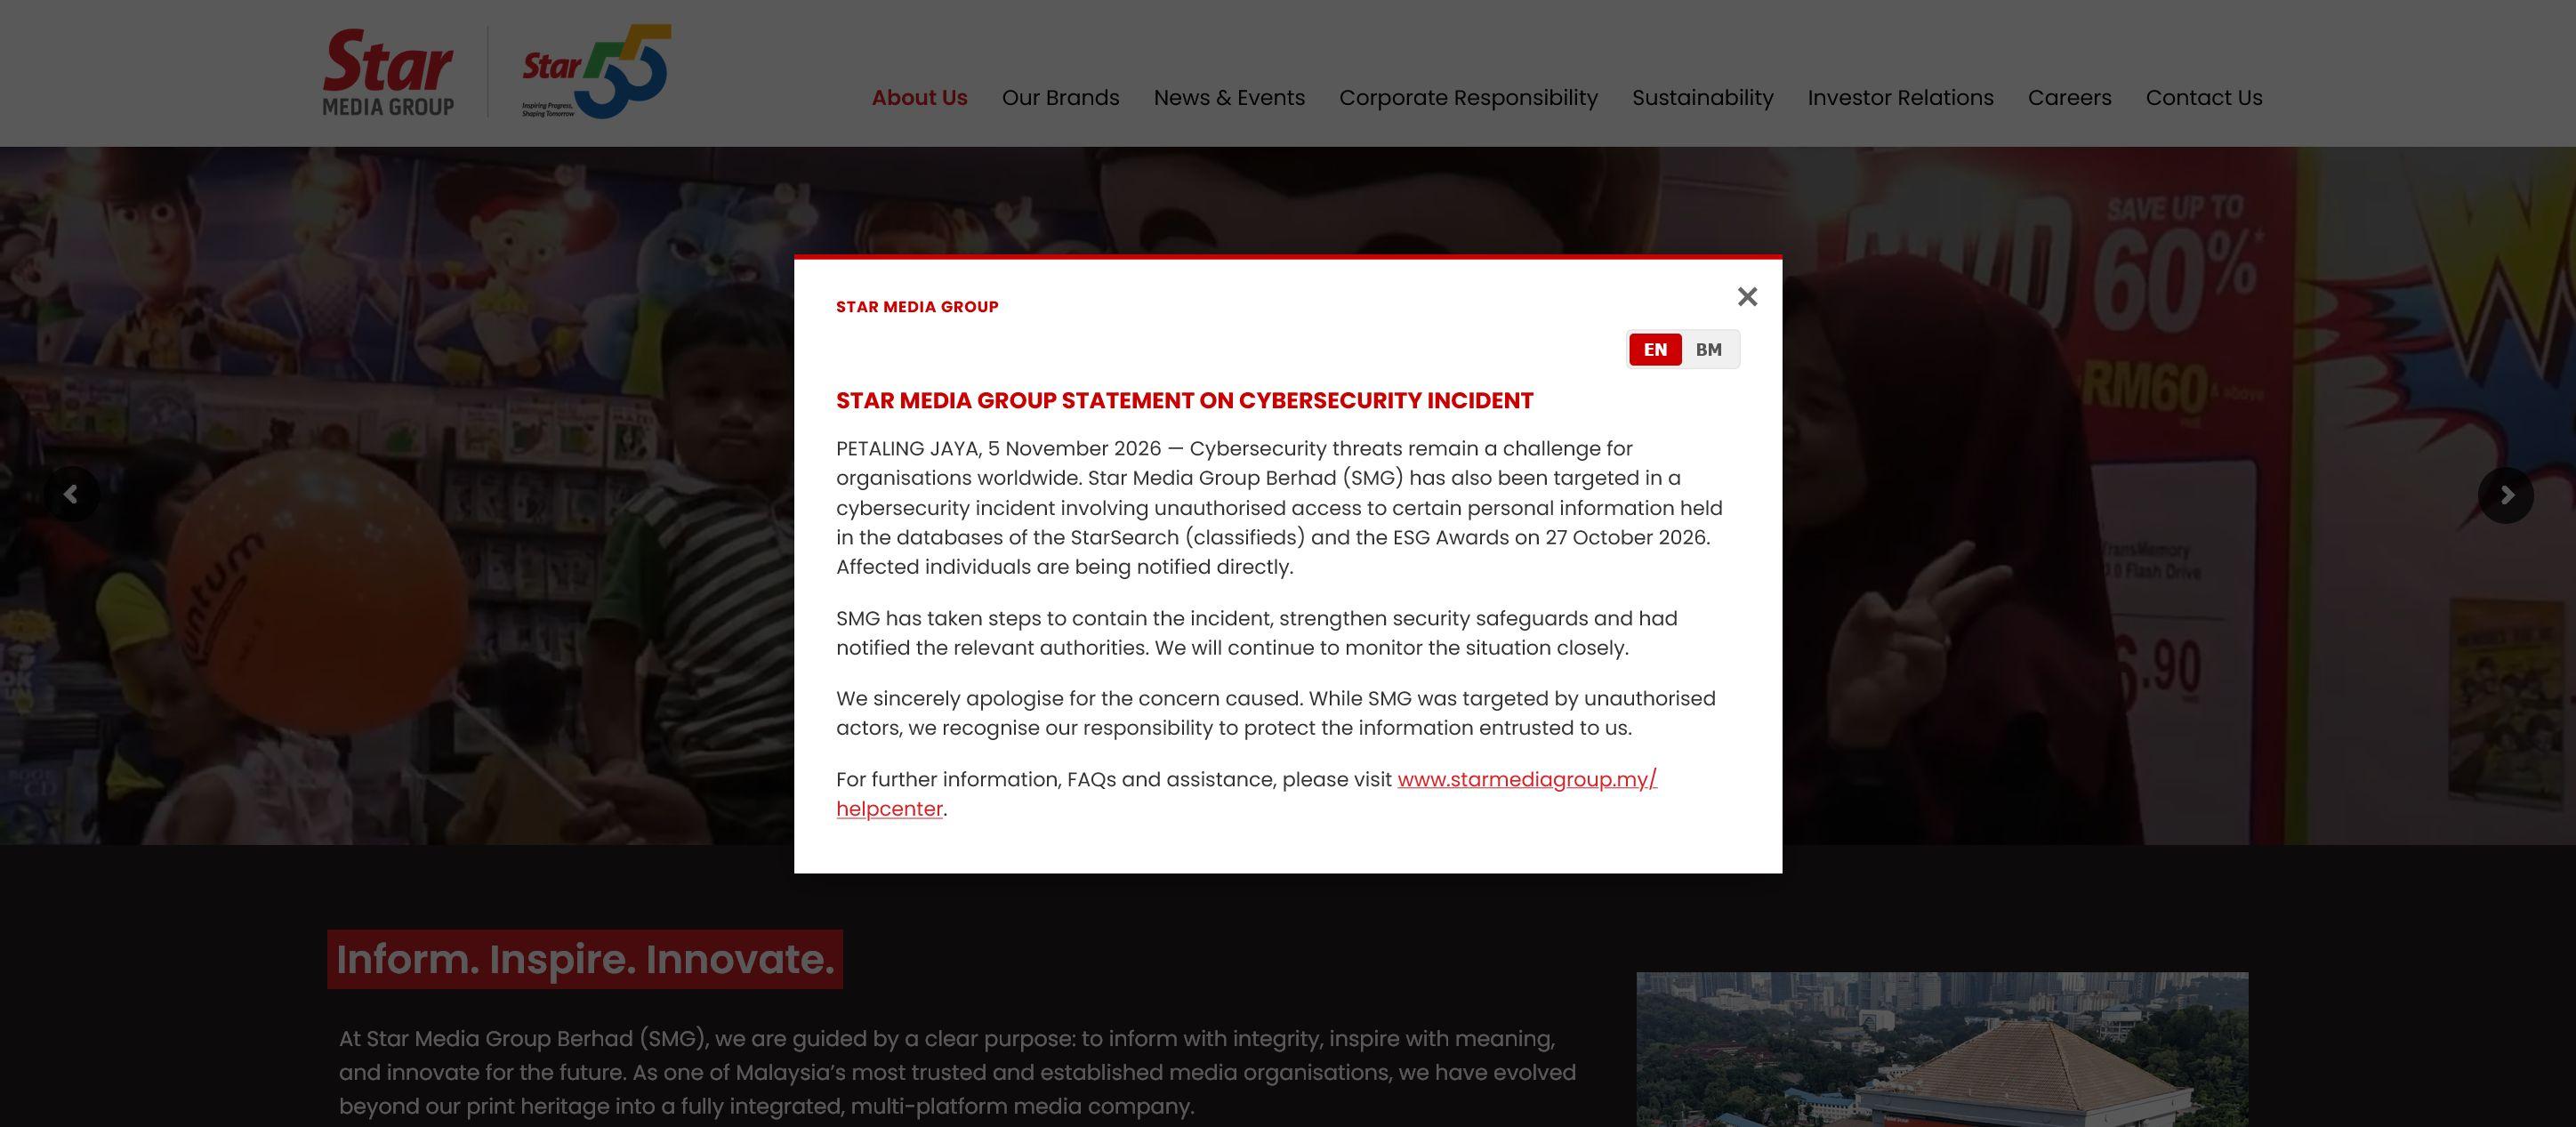
The cybersecurity incident affected two of the company’s databases, StarSearch classifieds and ESG Awards. Star Media Group confirmed that personal information was stolen on 27 October 2026 and publicly disclosed the incident on 5 November.
The company said the attackers exploited a vulnerability in one of its applications to gain unauthorised access.
Affected individuals began receiving notifications on 4 November. Star Media Group has also launched a dedicated website where users can check whether their email addresses were affected by the breach.
The company has not disclosed how many individuals were affected or how much personal information was stolen.
What Personal Data Was Stolen in the Star Media Group Breach?
According to Star Media Group’s official disclosure, the breach involved two databases containing different types of personal information.
The StarSearch classifieds database contained first names, last names, addresses, states, countries, telephone numbers, email addresses and Malaysian identity card numbers (NRIC).
The ESG Awards database contained first names, last names, mobile telephone numbers, email addresses and passwords.
Star Media Group confirmed that these records were exfiltrated, meaning they were copied from its systems without authorisation.
The company said ESG Awards passwords were stored in encrypted form. However, it has not disclosed the encryption or hashing method used to protect them.
Without those technical details, it is not possible to independently assess how resistant the stolen passwords would be to attempts to recover them.
Star Media Group said the two affected databases did not contain bank account numbers or payment card information.
Nevertheless, stolen personal information such as NRIC numbers, telephone numbers and residential addresses could potentially be used in phishing attempts, identity fraud and scams.
Was The Star News Website Also Affected?
Star Media Group operates The Star newspaper and TheStar.com.my news website, but the company has identified only its StarSearch classifieds and ESG Awards databases as affected by the cybersecurity incident.
In its official FAQ, the company said these were the only databases affected and that it had maintained data integrity throughout the rest of the group. There has been no confirmation that the main TheStar.com.my subscriber database or its associated news subscription accounts were compromised.
The company has also not announced a general password reset for all The Star news subscribers.
The distinction is important because the breach notifications refer to Star Media Group, which operates several services beyond its main news publication.
Users Report Receiving Data Breach SMS and Email Notifications
Some Malaysians reported receiving SMS and email notifications about the incident before the company’s public statement.
In a discussion on the r/malaysians Reddit community, users shared their experiences receiving notifications from Star Media Group.
One user reported receiving an SMS despite having an old account, while another said they received both an email and an SMS containing information about the breach.
Other users questioned whether the notifications were genuine.
Star Media Group’s official Help Centre confirms that notifications were sent to affected individuals beginning 4 November 2026.
The company has advised recipients to visit its official website directly rather than relying on links in unexpected messages.
ESG Awards Users Required to Reset Their Passwords
Star Media Group is requiring affected ESG Awards users to reset their account passwords as a precautionary security measure.
The company said users should visit the official ESG Awards website and enter their registered email address and existing password on the login page.
The system will then send a password reset email to their registered email address. The password reset link will expire after one hour.
Affected users are also advised to change their passwords on other websites or online services if they have reused the same credentials.
The company recommends using unique passwords for different accounts and enabling two-factor authentication wherever available.
Although the stolen ESG Awards passwords were stored in encrypted form, Star Media Group has not provided enough technical information to determine how securely the credentials were protected.
Star Media Group Notified Malaysia’s Data Protection Regulator
Star Media Group confirmed that the personal data theft occurred on 27 October 2026.
Three days later, on 30 October, the company notified Malaysia’s Personal Data Protection Commissioner about the incident. It said a Data Breach Notification was submitted under Section 12B of the Personal Data Protection Act (PDPA). A police report was also lodged with the Royal Malaysia Police (PDRM).
Star Media Group has engaged independent cybersecurity specialists to investigate the breach and review the affected systems.
The company said it had contained the incident and was implementing additional security measures, including stronger access controls, authentication safeguards, security updates and monitoring.
The attackers have not been identified, and their motive remains unknown.
As of the company’s FAQ update on 5 November 2026, Star Media Group said it had not received any ransom demand or other demands relating to the incident.
The company has not disclosed the specific application vulnerability that was exploited or whether the stolen information has subsequently appeared on underground data marketplaces.
How to Check Whether Your Personal Data Was Leaked
Star Media Group has established an official Help Centre for individuals who want to check whether their email addresses were affected.
The website is available at:
https://www.starmediagroup.my/helpcenter/
Users can enter their email addresses into the checking tool to determine whether they were included in the affected records.
The company has warned that it will never ask individuals to disclose account passwords, banking one-time passwords (OTPs) or credit card numbers in connection with the breach.
Affected individuals should also be cautious of suspicious telephone calls, SMS, WhatsApp messages and emails claiming to represent banks, government agencies or telecommunications providers.
This is particularly important for individuals whose NRIC numbers and addresses were exposed, as scammers could use such information to make fraudulent communications appear legitimate.
For further assistance, Star Media Group has provided a dedicated email address at [email protected] and a hotline at 1300 88 7827.
The hotline operates from 9am to 5pm daily until 13 November 2026. It will subsequently operate during the same hours on weekdays.
Star Media Group said its investigation is continuing and that additional information will be published through its official Help Centre as updates become available.
(PDF copy) – Star Media Group FAQ
Note: In its 2025 Annual Report, Star Media Group stated that it experienced no successful cybersecurity breaches during the financial year, despite facing frequent hacking and phishing attempts. The company also reported that external penetration testing by third-party specialists identified only low-risk vulnerabilities, all of which were promptly addressed.
The company has not disclosed whether the application vulnerability exploited in the October 2026 data breach was previously identified during its security assessments.
On 3 November 2026, Prime Minister Datuk Seri Anwar Ibrahim warned in Parliament that Malaysia could become a target of sophisticated cyberattacks amid growing international cybersecurity threats. Following his warning, the National Cyber Security Agency (NACSA) raised Malaysia’s National Cyber Security Threat Level from Low to Medium on 4 November as a precautionary measure. The government has also called for stronger cybersecurity preparedness across critical sectors, including banking and essential services. There is no confirmed connection between the government’s warning and the Star Media Group data breach.
0
Tagged: ESG Awards, Malaysia cybersecurity, password leak, Star Media Group, Star Media Group data breach, StarSearch, The Star
- You must be logged in to reply to this topic.